- SOC 2
- Audit-Ready. Business Confidence.
SOC 2 Certification for a Stronger, More Trusted Business
- Practical Guidance
- Experienced Auditors
- Focused On Your Goals
- SOC 2
- Audit-Ready. Business Confidence.
SOC 2 Certification for a Stronger, More Trusted Business
- Practical Guidance
- Experienced Auditors
- Focused On Your Goals
SOC 2 Type I
Evaluate whether controls are suitably designed as of a specified date.
SOC 2 Type II
Evaluate control design and operating effectiveness over an observation period.
Flexible Trust Services Criteria
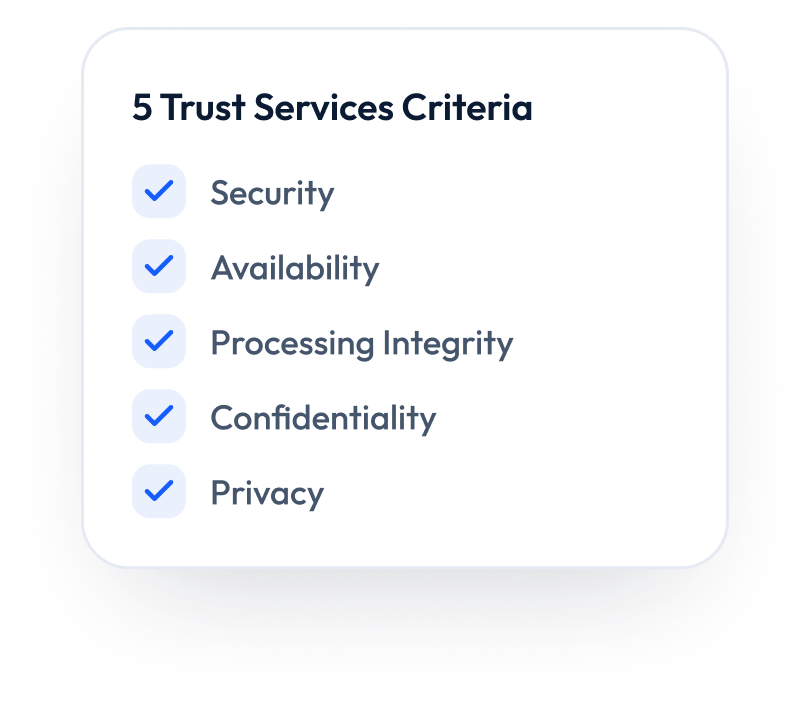
Scope Security, Availability, Confidentiality, Processing Integrity and Privacy based on your requirements.
Independent Attestation
Receive a formal SOC 2 report following examination by an independent licensed CPA / CPA firm.


What is SOC 2?
More than a report.
It’s a competitive advantage.
SOC 2 helps you demonstrate trust, win customers, and unlock new business opportunities.
The Five Trust Services Criteria
Security
Protection of systems and information from unauthorized access.
Availability
Systems are available for operation and use as committed.
Processing Integrity
Systems process information completely, accurately and on time.
Confidentiality
Sensitive information is protected as committed.
Privacy
Personal information is collected, used, retained and disclosed as committed.
SOC 2 Type I vs Type II
Type I
Design and Readiness
- Assesses control design
- Point-in-time evaluation
- Useful for early-stage or time-sensitive needs
Type II
Operating Effectiveness
- Assesses design and operating effectiveness
- Covers a defined period (typically 3–12 months)
- Provides greater assurance to customers and enterprises
Your SOC 2 Journey with GCAI
Scope & Planning
Understand your business, define scope and readiness.
Readiness & Gap Assessment
Review controls, policies and evidence. Address gaps.
Audit Execution
Independent CPA firm conducts the SOC 2 audit (Type I or Type II).
Report & Findings
Receive the draft report and address any findings (if applicable).
Final SOC 2 Report
Receive your SOC 2 attestation report to share with customers and stakeholders.
Build Trust. Unlock Opportunities.
Win More Customers
Meet security and compliance requirements of enterprise clients.
Strengthen Governance
Build robust internal controls and operational discipline.
Mitigate Risk
Identify and address risks across your systems, people and processes.
Demonstrate Transparency
Show your commitment to protecting customer data and privacy.
What Our Clients Say
Priya Sharma
CEO, CloudSync
Daniel Kim
CTO, NexaTech
Emily Carter
COO, FinMate
What Our Clients Say
Is SOC 2 a certification?
How long should the SOC 2 Type II observation period be?
Do we need to include all five Trust Services Criteria?
How often should SOC 2 be renewed?
How long does a SOC 2 audit take?
Ready to Start Your SOC 2 Journey?
Get a clear scope, timeline and audit plan from our team.